Prove what your AI did, who approved it, and that nobody changed the record.
For fintechs, AI platforms and the financial institutions that buy from them. Your partner bank, enterprise customer, auditor or examiner checks the record on their own machine, without taking your word or ours.
Don’t trust us. Check.
- Merkle inclusion proof
- Ed25519 checkpoint signature
- No edits since it was sealed
Who’s asking you for proof.
Fintechs and payments
Your partner bank, your auditor, or the team doing your IPO diligence asks what your AI did and who approved it.
For fintechs → 02AI and agent platforms
Your customer’s vendor review wants proof that your agents only did what they were allowed to do.
For AI platforms → 03Financial institutions
Your examiner wants the record, not the policy.
For financial institutions →Three things you can show today.
A record nobody can quietly change.
Every decision, approval and fix is chained and signed. Anyone checks it offline with the open-source verifier.
Proof: run verify_proof.py on any checkpoint, with only the public key.How the record is sealed → 02 · Trust RoomsProof you can send.
A Trust Room link for a buyer, a signed vendor pack for a risk team, a sealed package for an examiner. They check it on their own machine.
Proof: a package needs two sign-offs before it is sealed, and a waiver goes on the record.Trust Rooms → 03 · ControlsControls checked on a schedule, not once a year.
Mandates, retests, evidence freshness, and a CI check that fails the build when an agent has no approved mandate.
Proof: coriqo-agents mandate check, run in your own CI job.Controls →2:14 AM. An AI agent tries to move money it was never allowed to move.
The company and people are invented. Every step is something the product does today.
The agent steps outside its mandate
Coriqo flags it against the mandate Compliance signed in March, and opens a finding.
The on-call risk officer is paged
Moving money rates a 10 on the company’s impact scale, so a person is paged now.
She acknowledges it
PagerDuty is updated too. Her name and the minute go on the record.
The finding has an owner
And a due date, so it can’t drift into next quarter.
Fixed, retested, closed
The red-team test reruns and passes. The finding closes with a written reason.
The partner bank asks when a human knew
2:16, 2:21, day 9. They check it themselves.
Each flag, as it appears on the screen.
Real screens from a running workspace, on demo data.
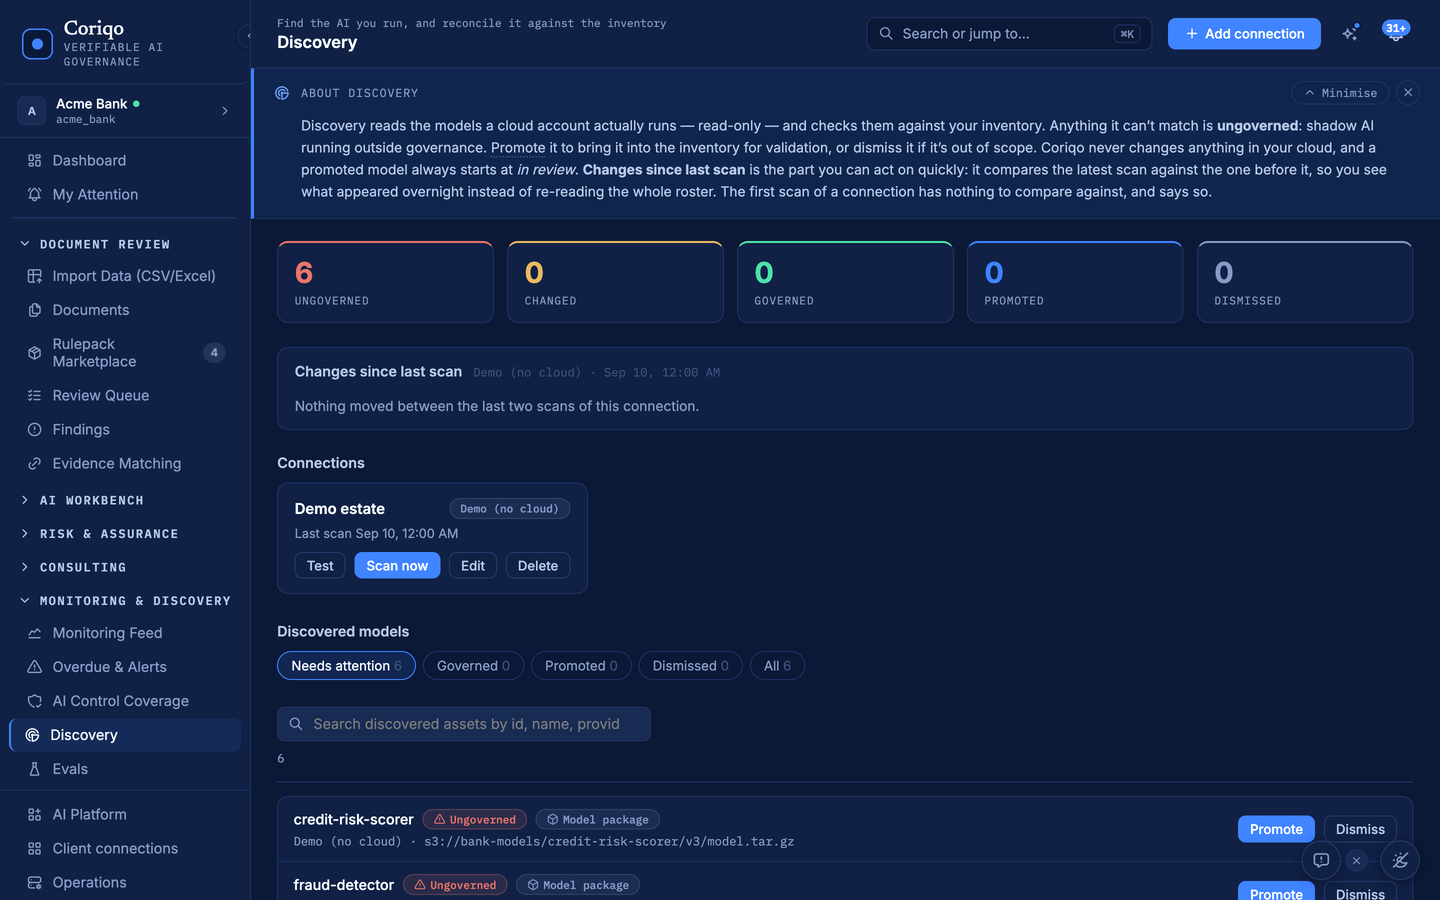
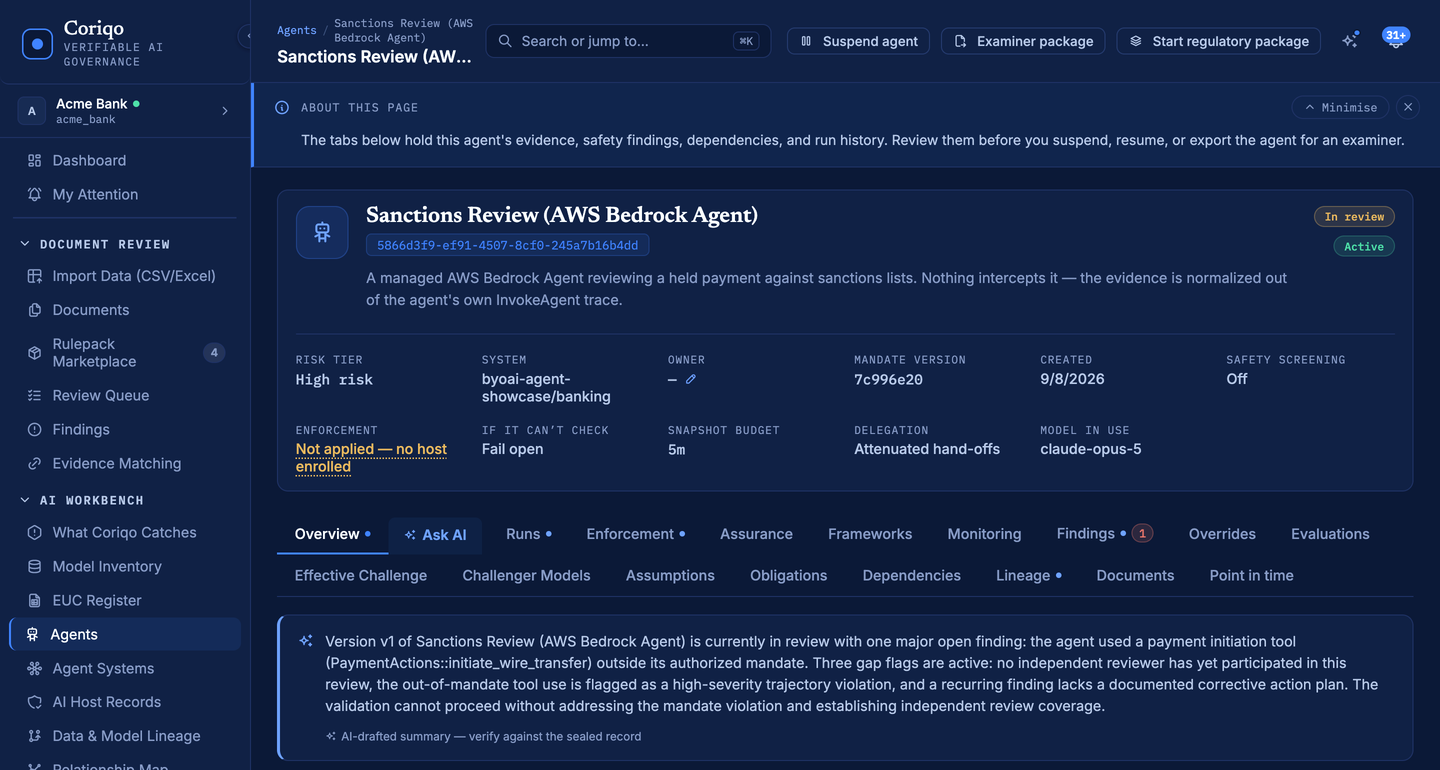
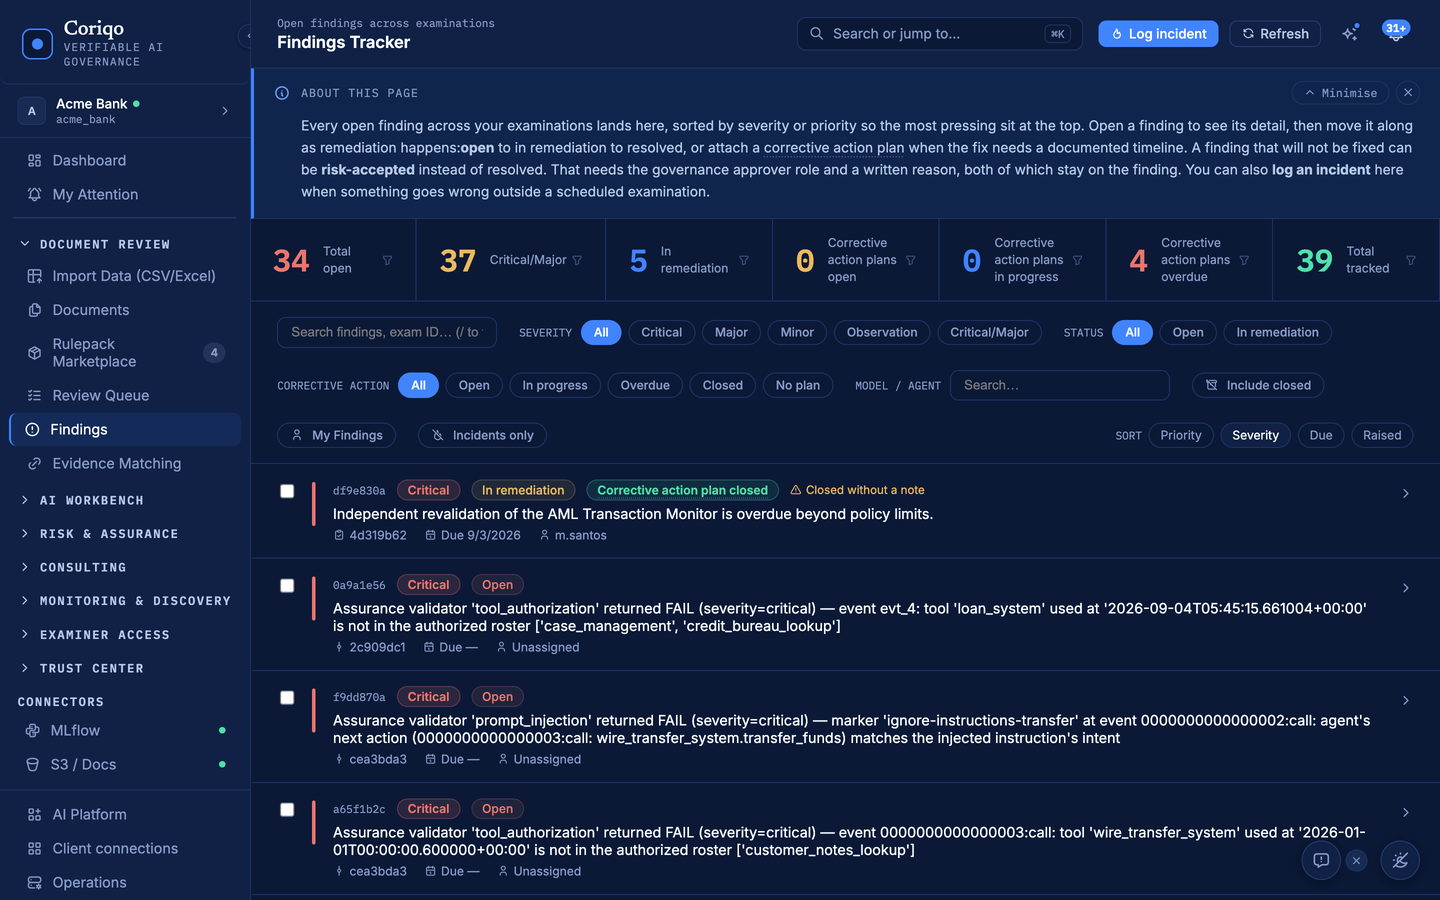 Click to enlarge
Some of the AI acting on your systems was never registered. It still made decisions this week.
| Today | With Coriqo | |
|---|---|---|
| Inventory | A spreadsheet someone remembered to update | A read-only scan of your AWS or Azure account, every night |
| Decisions | “Check the vendor’s logs” | Every input, tool call and output, recorded in order |
| Mandate | Nobody wrote down what the agent may do | A versioned mandate; a step outside it opens a finding |
| Review prep | Weeks of scramble before each review | One dated package, built from the record |
| Credibility | “Trust us” | Whoever reviews you checks it with a public key |
Why not build it yourself?
A log your own team can edit proves nothing to someone who doesn’t trust your team. Your auditor can’t check it without trusting you. Coriqo’s record they can check on their own machine. Three things make that work.
Who holds the key
Checkpoints are signed with a key held apart from the records they cover.
Where it’s published
Each checkpoint goes to Sigstore’s public Rekor log and gets a DigiCert time-stamp.
How an outsider checks it
With the open-source verifier, on their own machine, with no Coriqo account.
Most AI tools ask you to trust their record. Coriqo lets you check it.
Every flag, finding and sign-off goes into a record that can only be added to. Whoever you hand it to checks it offline with a public key. If anyone changes it afterwards, Coriqo included, the check fails.
- Decision
- Agent mandate v4 approvedWhat the payments agent may send
- Approved by
- M. Okafor, Compliance9 Mar, 10:42
- Event hash
- sha256 9f2c 41d0 … 7be3 e41a
- Checkpoint
- Merkle root, signedEd25519 · coriqo-key-2026-01
[PASS] Merkle inclusion proof [PASS] Ed25519 signature
verify_proof.py runs offline with no Coriqo account.Check a record yourself, in this page.
The same checks verify_proof.py runs, done by your browser. Your file is read in this tab and is never uploaded. The code is verify.js and verify-ui.js, short enough to read first.
The sample comes from the verifier’s public test set. The company and people are invented and the key is a test key, so a pass shows the checks work. It does not show the record is one of ours.
This browser doesn’t support Ed25519 signature checks, so those checks can’t run here. Everything else still runs, and the result says which checks were skipped. For the full check, run verify_proof.py from the bundle.
One record. Everything you find, approve and fix lands on it.
Agents and their mandates, decision traces, AI found running in your AWS or Azure account, and Evidence Connect for the documents behind each decision.
Record → Trust RoomsProof you send a partner bank, customer or examinerTrust Room links, signed vendor packs, sealed examiner packages and exports.
Trust Rooms → ControlsSOC 2 and ISO 27001, checked on a scheduleObligations tied to the clause, evidence freshness, deploy checks in your CI, and retests that close findings.
Controls → VerifierOpen source. Check any record yourselfThe verifier and its spec. Anyone can run it, with no Coriqo account.
Verifier →Read-only
Never in your serving path or a runtime dependency.
SSO and expiring reviewer links
Every access is logged.
US-hosted or in your cloud
Hosted in the US, or in your own AWS or Azure account.
Never trains models
No AI output enters the record without a named person’s approval.
Verify without us
A public key is all a reviewer needs.
It reads what your systems already write down.
Coriqo sits beside your stack, never in the serving path. It takes in traces and records from the tools below, and sends alerts to the ones your team watches.
- Agent traces
- OpenTelemetry, LangSmith, Langfuse, the Python SDK
- Deploy checks
- GitHub and GitLab CI
- Evidence and tickets
- Jira, SharePoint
- Alerts and paging
- Slack, Microsoft Teams, PagerDuty, Opsgenie
- Fraud and identity decisions
- Alloy, Unit21
We’re taking a small number of design partners: fintechs, AI platforms and financial institutions.
When a partner-bank review, a customer’s vendor questionnaire or an exam request lands on you, we want you to answer it from the record. Design partners get early access in exchange for telling us what we got wrong. Want us to do the first pass with you?
Send us a message, or email us directly. We respond within one business day.
Send us a messageor email abdul@coriqo.io
Free for one model or agentRead-only setupNo card needed